Turn Fedora into a pentest machine.
Pendora is a modular installation framework that transforms a standard Fedora Linux install into a penetration testing and security assessment VM — bringing Kali's toolset, workflows, and aesthetics to Fedora's modern Wayland, RPM/DNF, and systemd ecosystem.
$ git clone https://github.com/sec-moose/pendora && cd pendora && ./install.sh --basic▊// architecture
Four tiers. Human-editable. Fully modular.
Tooling, services, and configuration are organized into dedicated tiers — each a plain list you can read, edit, and extend.
Native DNF RPMs
pkg-lists/
109 packages verified against official Fedora repos — base compilers, networking, sniffers, web discovery, reversing, and forensics.
Pipx Isolated Tools
pipx-lists/
Offensive Python utilities in isolated environments, safe from system library conflicts.
Upstreams & Containers
upstreams/
Vendor installers, git clones, and Docker containers for enterprise suites.
Shell & Look-and-Feel
zsh/
Interactive Zsh with autosuggestions, syntax highlighting, completions, and pentesting aliases.
// install
Keep GNOME, or go full tiling.
All three modes are tested and verified on Fedora Workstation VMs. Installing Sway never removes GNOME — pick your session at the GDM login screen.
Basic Pentest
./install.sh --basic (-b)Keeps your default Fedora GNOME desktop intact while deploying all pentest CLI tools (00–60), Pipx tools, Docker container suites, Zsh, Neovim, and Alacritty. Zero desktop changes.
Sway Desktop
./install.sh --sway (-W)Lightweight Sway tiling compositor with the Noctalia shell, Hack Nerd Font, focus-based window opacity, and SPICE host/guest clipboard sharing. 100% native Fedora RPMs — zero COPR repos. Switch between GNOME and Sway at the login screen.
Full Install
./install.sh --all (-a)Single-pass end-to-end deployment of everything in Basic plus the full Sway desktop stack (70-sway.list, dotfiles, screensharing portal services).
// preview
Two desktops. One framework.
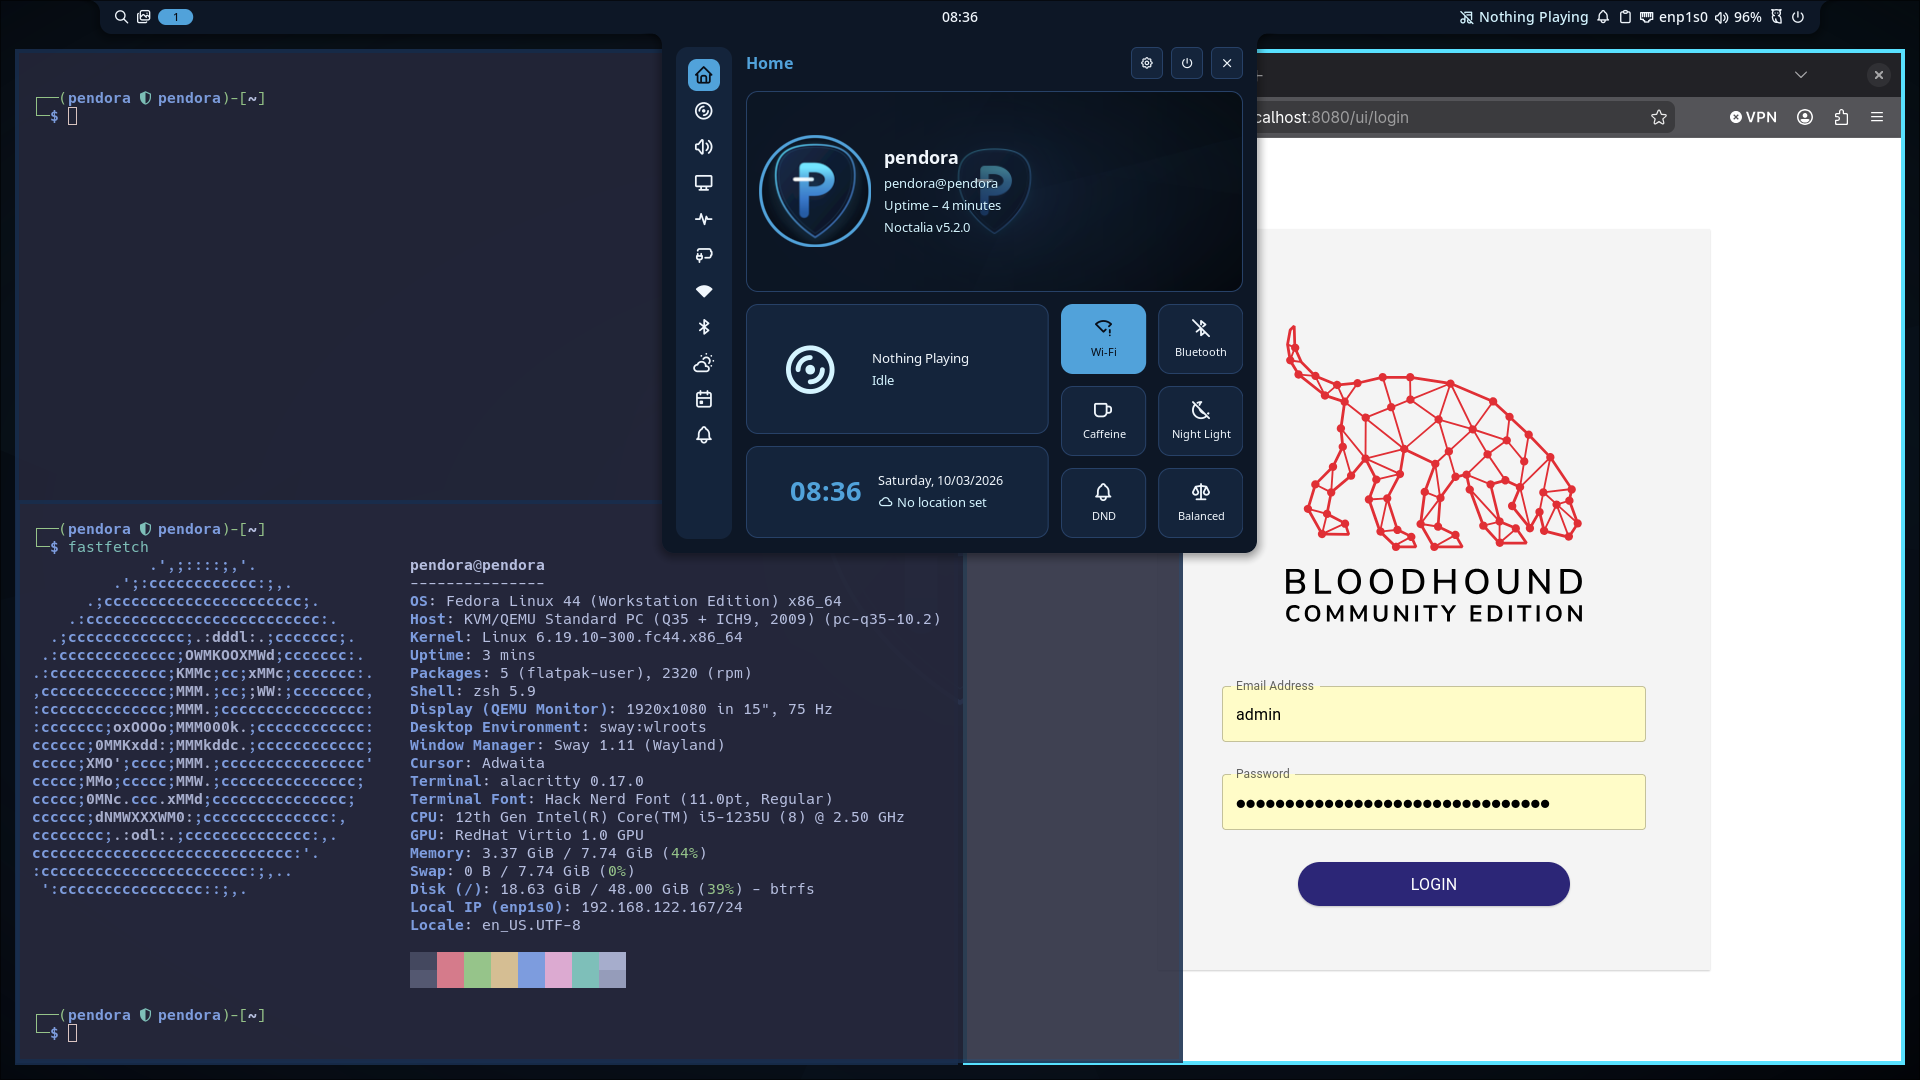
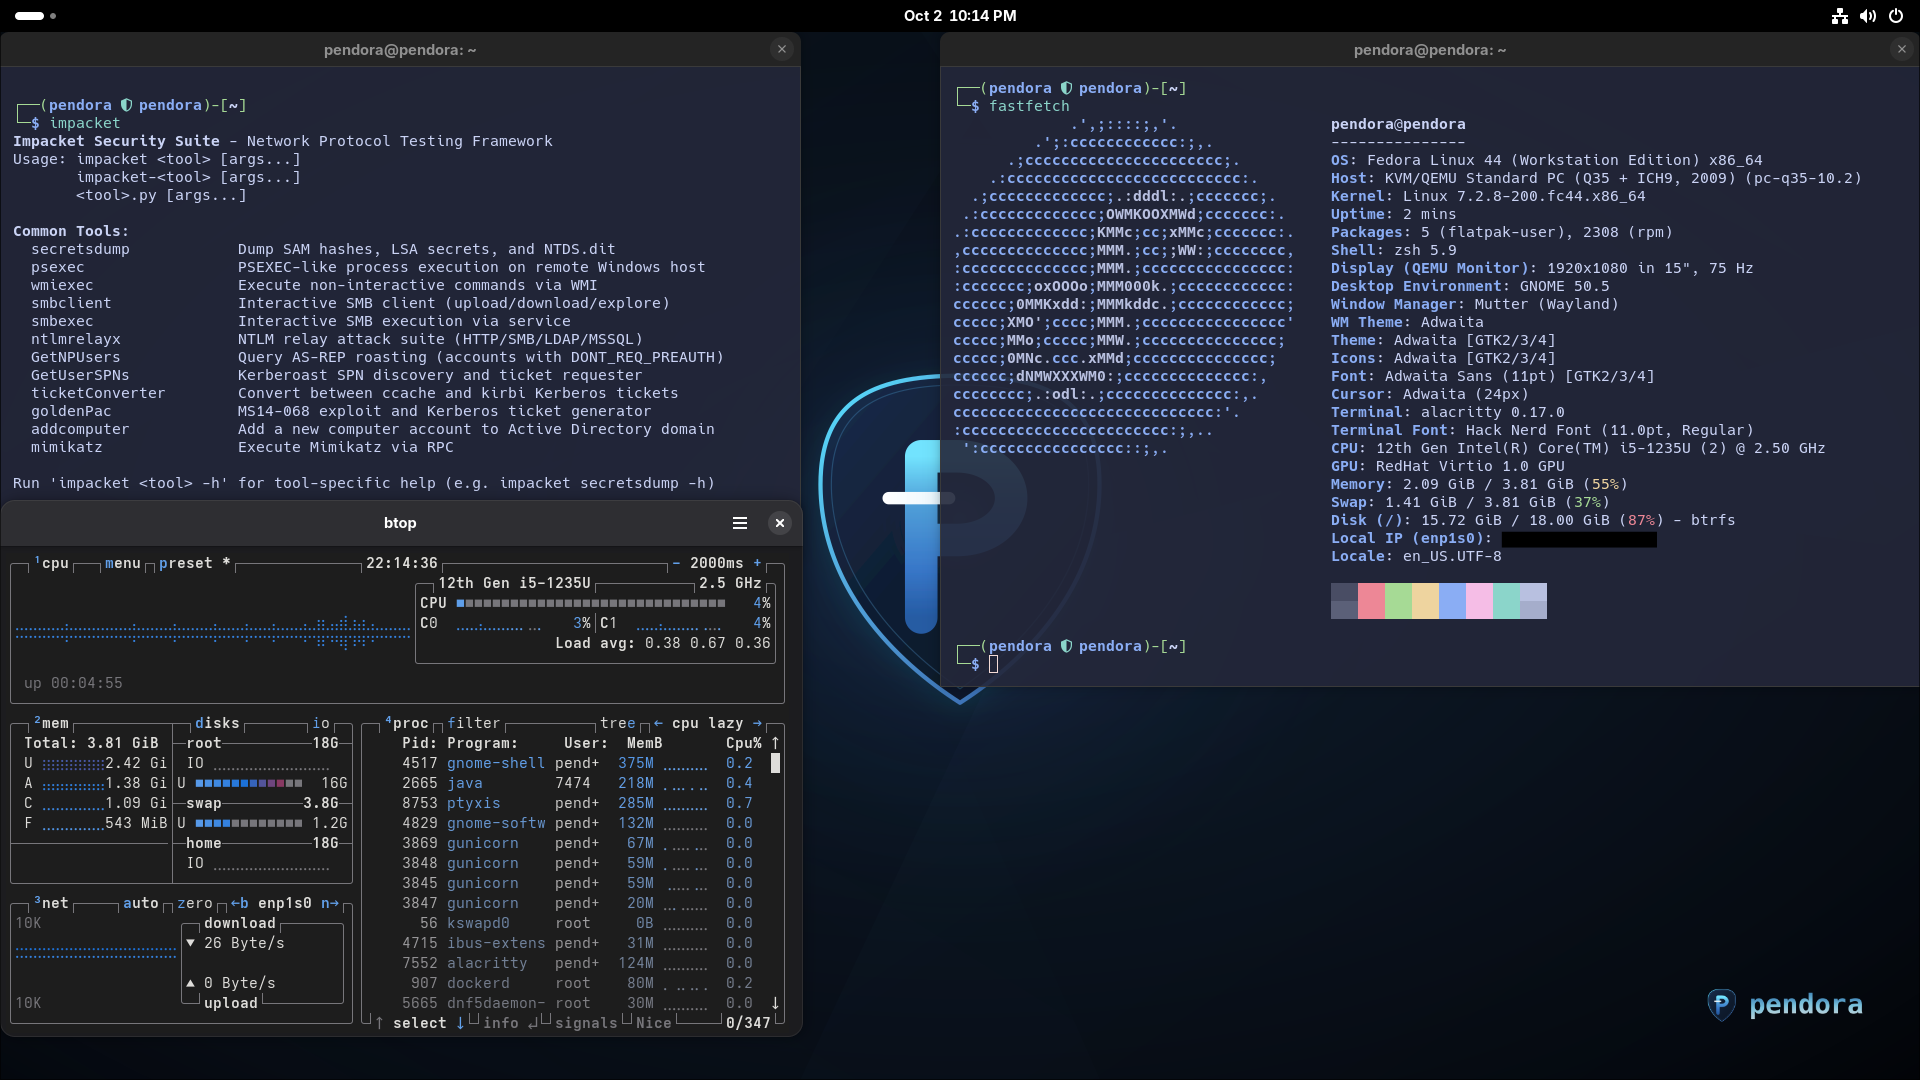
Keep Fedora's GNOME with --basic, or deploy the dynamic Sway tiling desktop with --sway — both tested and verified on QEMU/KVM.
$ --sway — Sway dynamic tiling desktop (Noctalia shell + Catppuccin Alacritty + focus opacity)
$ --basic — Fedora GNOME pentest desktop
// dashboards
Containerized suites, ready on localhost.
Portainer
localhost:7999work in progressSysReptor
localhost:8000BloodHound
localhost:8080Use entirely at your own risk
Pendora is provided "as is" without warranty of any kind. Some upstream modules fetch and execute vendor installation scripts directly — inspect all scripts before running them. Parts of this project were developed with AI assistance. Intended for authorized security testing and lab environments only.